AI & Technology
Agent Badge First
A plain-language AI engineering note on separating ads from answers, using local models safely, and issuing short-lived tool credentials
Summary
At a glance
- Ad selection and AI answer generation should be separate, with only the minimum intent signal crossing the boundary.
- Local models reduce external data movement, but they do not automatically make file, shell, or network permissions safe.
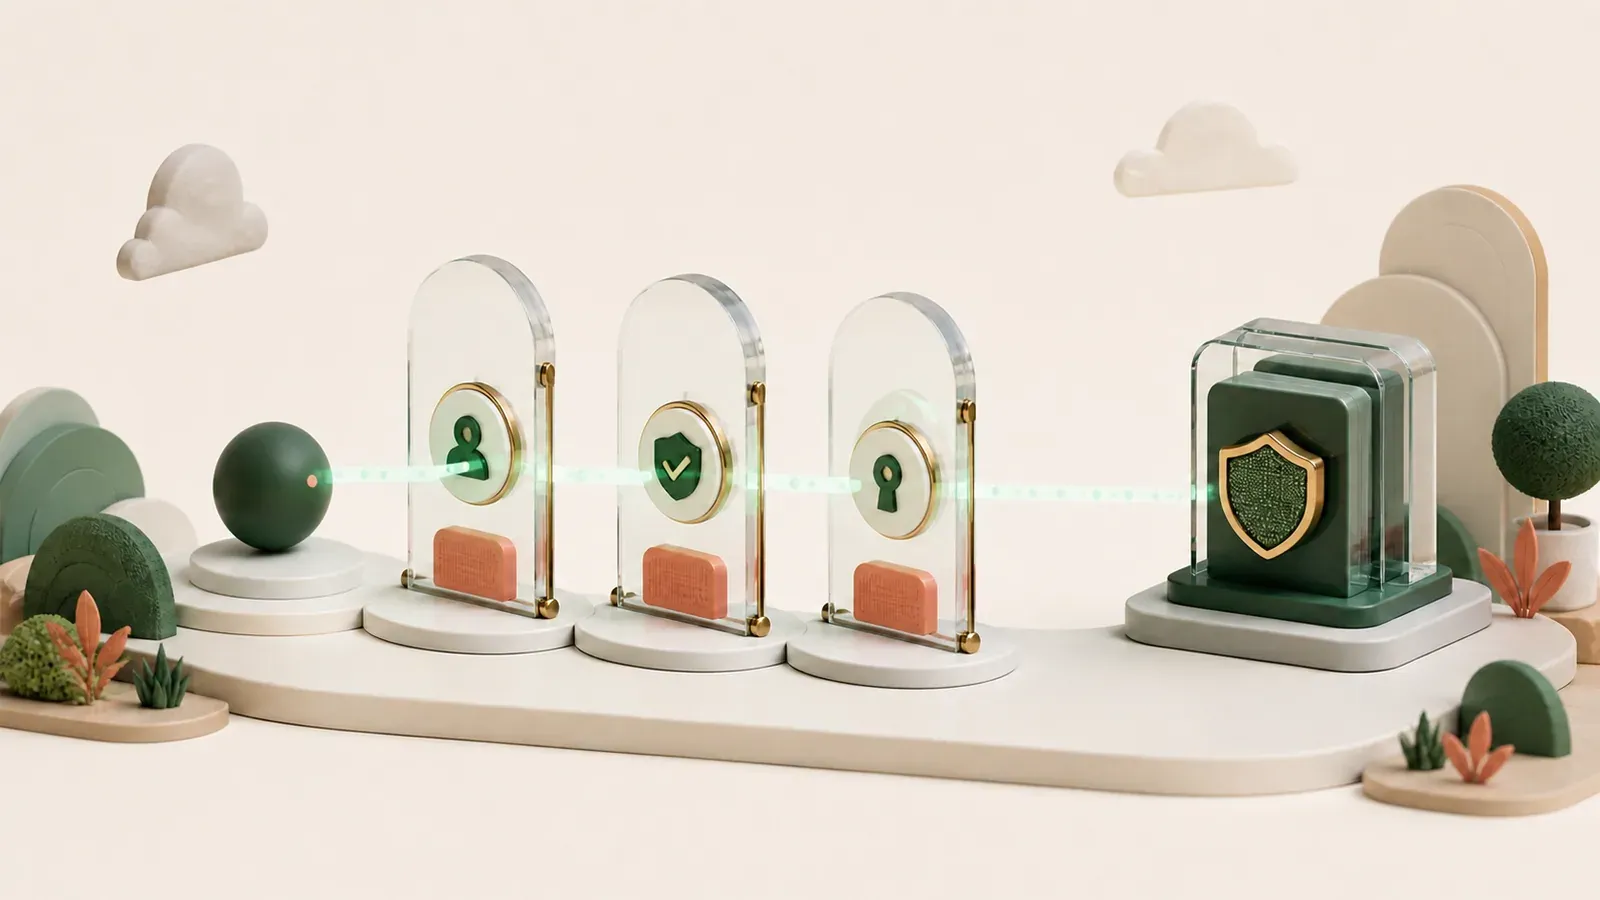
- External tool access should pass identity, policy, short-lived credentials, and an auditable event trail.
Data cutoff: the morning of August 12, 2026, Korea time
The technical items in today’s supplied briefing needed their dates corrected. OpenAI’s Korea ads expansion was announced in May, GitHub Copilot CLI local models in April, and Vercel Connect public beta in June. Put together, they still reveal one durable design rule: as agents become more capable, design the access badge before the connection.
Ordering one delivery does not require sending both the door code and a map to the property deed. An AI tool call should work the same way.
1. Put ads and answers on separate tracks
OpenAI says ChatGPT ads do not influence answers and conversations are not shared with advertisers. In a product, architecture—not a sentence in a policy—must enforce that promise.
I separate the paths like this:
user conversation -> answer model -> answer
minimum intent signal -> separate ad system -> ad area
- Do not put ad candidates into the answer prompt.
- Send only the needed intent category, not the raw conversation.
- Store answer logs and ad-impression logs for separate purposes.
- Let users disable personalization and delete relevant records.
- Label paid placement clearly in the interface.
If answers and ads simmer in the same pot, explaining which ingredient changed the taste becomes difficult.
Source: OpenAI’s ChatGPT ads pilot notice
2. A local model reduces one boundary, not every permission risk
GitHub Copilot CLI supports custom providers and local models such as Ollama and vLLM. Its offline mode can disable communication with GitHub servers and telemetry.
This can reduce the path by which sensitive code leaves the environment. It does not help if the local model can read every file, run every shell command, browse every internal service, and export results freely. Staying home is not the same as leaving every drawer open.
I restrict these separately from model location:
- readable work directories
- executable commands
- reachable network destinations
- session duration and call count
- whether outputs may leave the environment
Sources: GitHub Copilot CLI BYOK, local models, and offline mode, GitHub BYOK documentation
3. Issue a short-lived badge for every outside tool
Vercel Connect lets an app prove its identity with OIDC and request a provider token. The request can carry provider scopes, an installation target, resource restrictions, and provider-specific authorization details. The agent does not need to keep a long-lived provider secret in its environment.
My target flow is:
agent -> app identity -> policy check -> short-lived token -> external service
I also want an event trail for:
- who requested access
- project and environment identity
- scopes granted
- service and resources called
- expiration, refresh, and revocation
- success, failure, and retry counts
Keeping a master key in a better vault is not enough. If it leaks, it remains a master key. I want a key that opens a smaller door for a shorter time.
Sources: Introducing Vercel Connect, Vercel Connect implementation guide
4. Build durable boundaries before unverified product switches
The supplied briefing named Daybreak Red and Blue, GHES 3.22, more than 100 Connect services, and a same-day observability release. The official material I found supports the broader Daybreak direction, local Copilot models, and short-lived Connect credentials, but not every date and product detail in that list.
I will not hard-code a switch that I cannot confirm exists. I will build the boundaries that survive product-name changes:
- separate answer generation from ad selection
- separate model access from tool permission
- place a gateway between local and external models
- use task-level least privilege and expiration
- allowlist network, file, and command access
- audit credential and tool use
My conclusion is: give the agent an access badge before a capability chart. Models can produce a demo; boundaries keep the service alive.
Leaving a reaction may store a random identifier in this browser to prevent duplicates.